Cyber Security Consultancy
We are a consultancy, not a product vendor: our job is to tell you where you are exposed, what to fix first, and to stand behind that advice in front of your auditor or board.
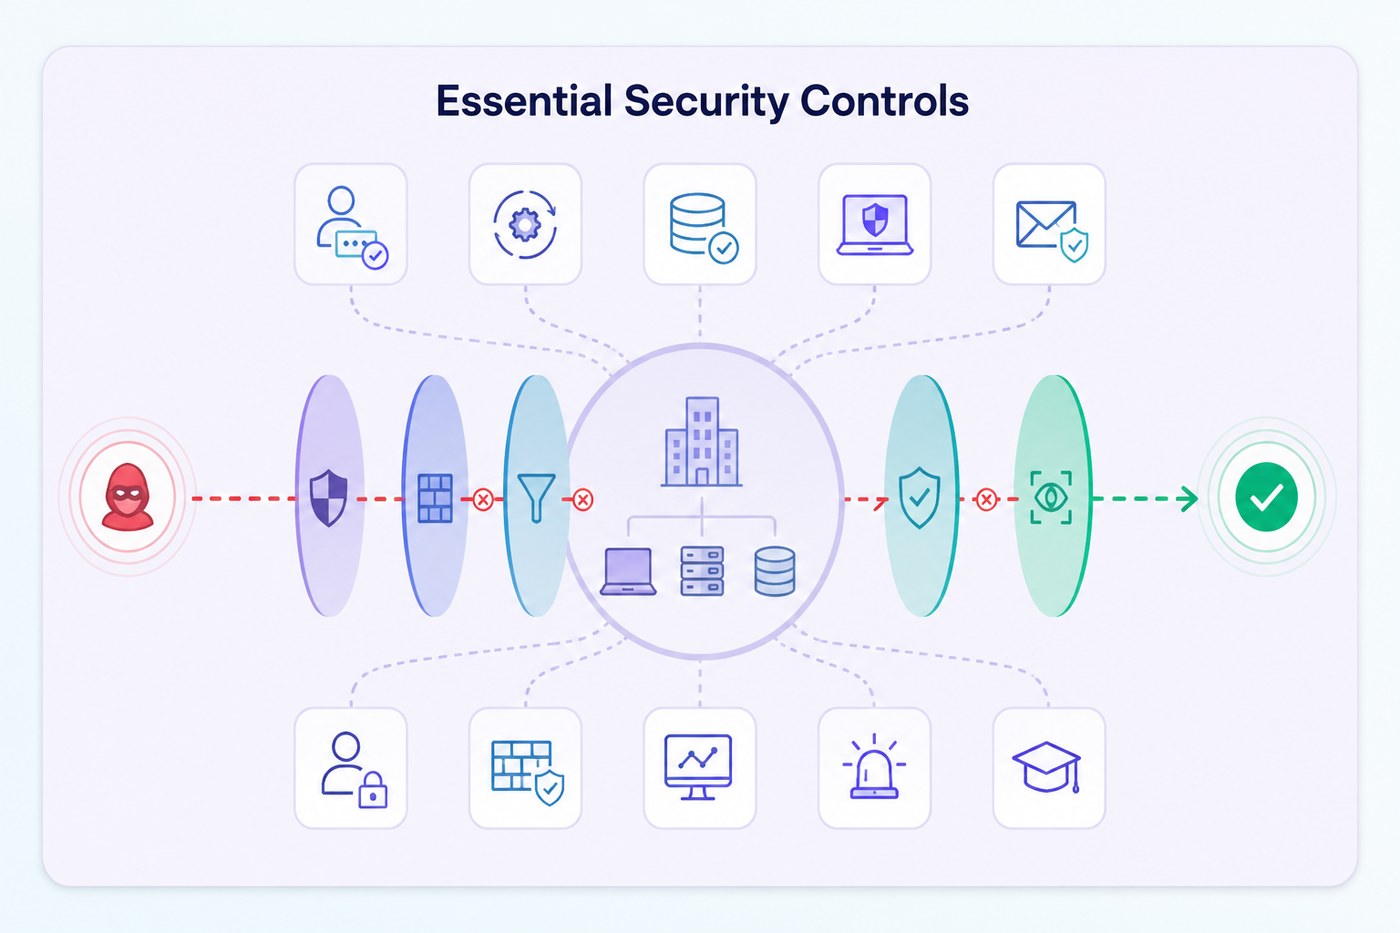
What is included
Security assessment
Your real exposure measured against the standard your sector expects, ending in a ranked, costed 90-day remediation plan.
Security audit & configuration review
A documented examination of the network, identity, endpoint and cloud configuration against a named standard, with every finding ranked by the exposure it actually creates.
Compliance readiness
PDPL security requirements and whatever your sector applies on top: policies, controls, internal audit and the evidence pack, ready for the certification body. The certificate is issued by an accredited body, not by us.
Security architecture review
Identity, network segmentation, cloud and remote-access designs reviewed and corrected.
Incident readiness
Response plans, tabletop exercises and retained support for when it happens.
Platforms we work with
Consultancy first: recommendations come with reasons and alternatives, and we say when you do not need something.
How we deliver
Baseline
Assessment against a recognised framework, showing where you actually stand.
Prioritise
A 90-day plan that closes the highest-impact gaps first.
Implement
Controls and policies delivered with your team or ours.
Prove
Evidence packs for auditors, regulators, clients and insurers.
What you can expect
- A ranked picture of exposure the board can read
- Controls implemented in priority order with evidence
- Certification achieved with an accredited body
- A security function that runs without heroics
What it changes for your business
Security spending fails when it is driven by fear or by whatever a vendor is selling that quarter. Consultancy exists to replace both with a ranked list, so every dirham closes the biggest open door first.
An illustration
An illustration, not an account of a past project: an 80-person firm is told by a key client to prove its security before contract renewal. The assessment finds the usual suspects: shared admin passwords, no MFA on email, a firewall nobody has patched, backups that were never restored once. Instead of a 60-page scare report, the firm gets a 90-day plan: six fixes in priority order, most delivered with its own IT provider, plus an evidence pack. The client questionnaire is answered line by line from that pack, and the renewal signs.
Frequently asked questions
Do you run a 24/7 SOC?
We do not operate a SOC ourselves. As consultants we define the requirement, run an independent selection of a managed-SOC provider, and oversee the service on your behalf.
Can you get us ready for a security certification?
We deliver the readiness work end to end: the gap review, the policies and controls, the internal audit and the evidence pack. The certificate itself is issued by an accredited body, which we help you select and prepare for.
How often should we audit our security?
At least annually, and after any significant change: a new platform, a major integration, an office move. Where a regulator, an insurer or a client contract requires a formal penetration test, that work is carried out by a specialist testing firm. We define the scope and the rules of engagement, appoint and supervise the tester, and then verify that every accepted finding has actually been closed.
Can you help during an actual incident?
Clients with incident-readiness retainers get priority response within the agreed SLA. Outside a retainer we assist where capacity allows and can coordinate specialist forensic providers, but the honest advice is to prepare the plan before you need it.
We have an IT provider already, why a separate security consultant?
Because the party that runs your systems should not be the only party marking its own homework. We review independently, they keep operating, and in our experience good providers welcome it, because the 90-day plan gives their work priorities and budget.
Start with a conversation
An initial consultation with a consultant rather than a salesperson, about your IT, security or systems question.